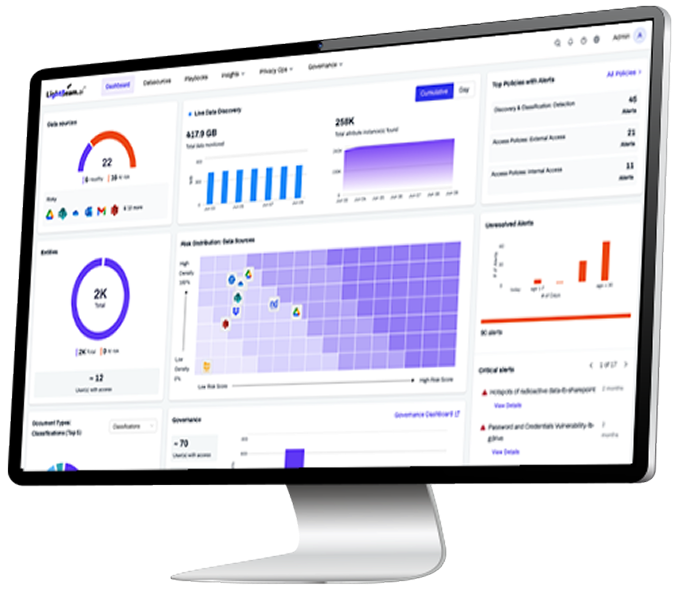
AI Governance That Enforces Agent Purpose
Govern AI use and agent actions by intended business purpose, with control over data, access, tools and consequential actions.

Permitted Access Isn’t Always Appropriate Access
Right-Size Human and Agent Access
Reveal users, groups, service accounts, copilots and agents with excessive sensitive data access, even across S3 and Salesforce, then revoke it automatically.
Stop Third-Party Exposure
Track all sensitive data shared with partners, knowing exactly whose data has been shared and how it’s being accessed.
Prove AI Governance
Deliver audit-ready evidence of who or what accessed sensitive data, which policy applied and why.
Lightbeam PrivilegeIQ
Automate Open Access Removal Across SharePoint, OneDrive & File Shares
Govern AI with Confidence, Control, and Accountability
90%
Reduction in Open Access
Reduce excessive access to sensitive data and enforce least agency across human and nonhuman identities.
80%
Fewer Compliance Violations
Strengthen AI governance with purpose-aware policies, automated controls, and continuous oversight.
70%
Faster Audit Completion
Accelerate access reviews and demonstrate accountability with automated reporting and audit evidence.
“Lightbeam gives us the ability to scan, classify, categorize, and label data so we can ensure that data does not go into areas it does not need to, including AI models.”
Patrick McKinney
VP of Security, Invisible Technologies
AI Governance and AI Usage Control for Agents
Purpose-Aware Context
Link every file to the person and business context it represents. The Data Identity Graph shows who or what has access, why, and whether that access fits its intended purpose.
Explore Data Identity GraphUsage Control at Machine Speed
Automated policies restrict or revoke excessive access, route approvals for high-risk actions and log every decision. No tickets, just immediate enforcement.
Explore Automated RemediationUnified Governance
One platform unifies discovery, classification, access governance and AI usage control. Integrated reports prove compliance and accelerate audits while cutting cost and admin overhead.
Explore Our Platform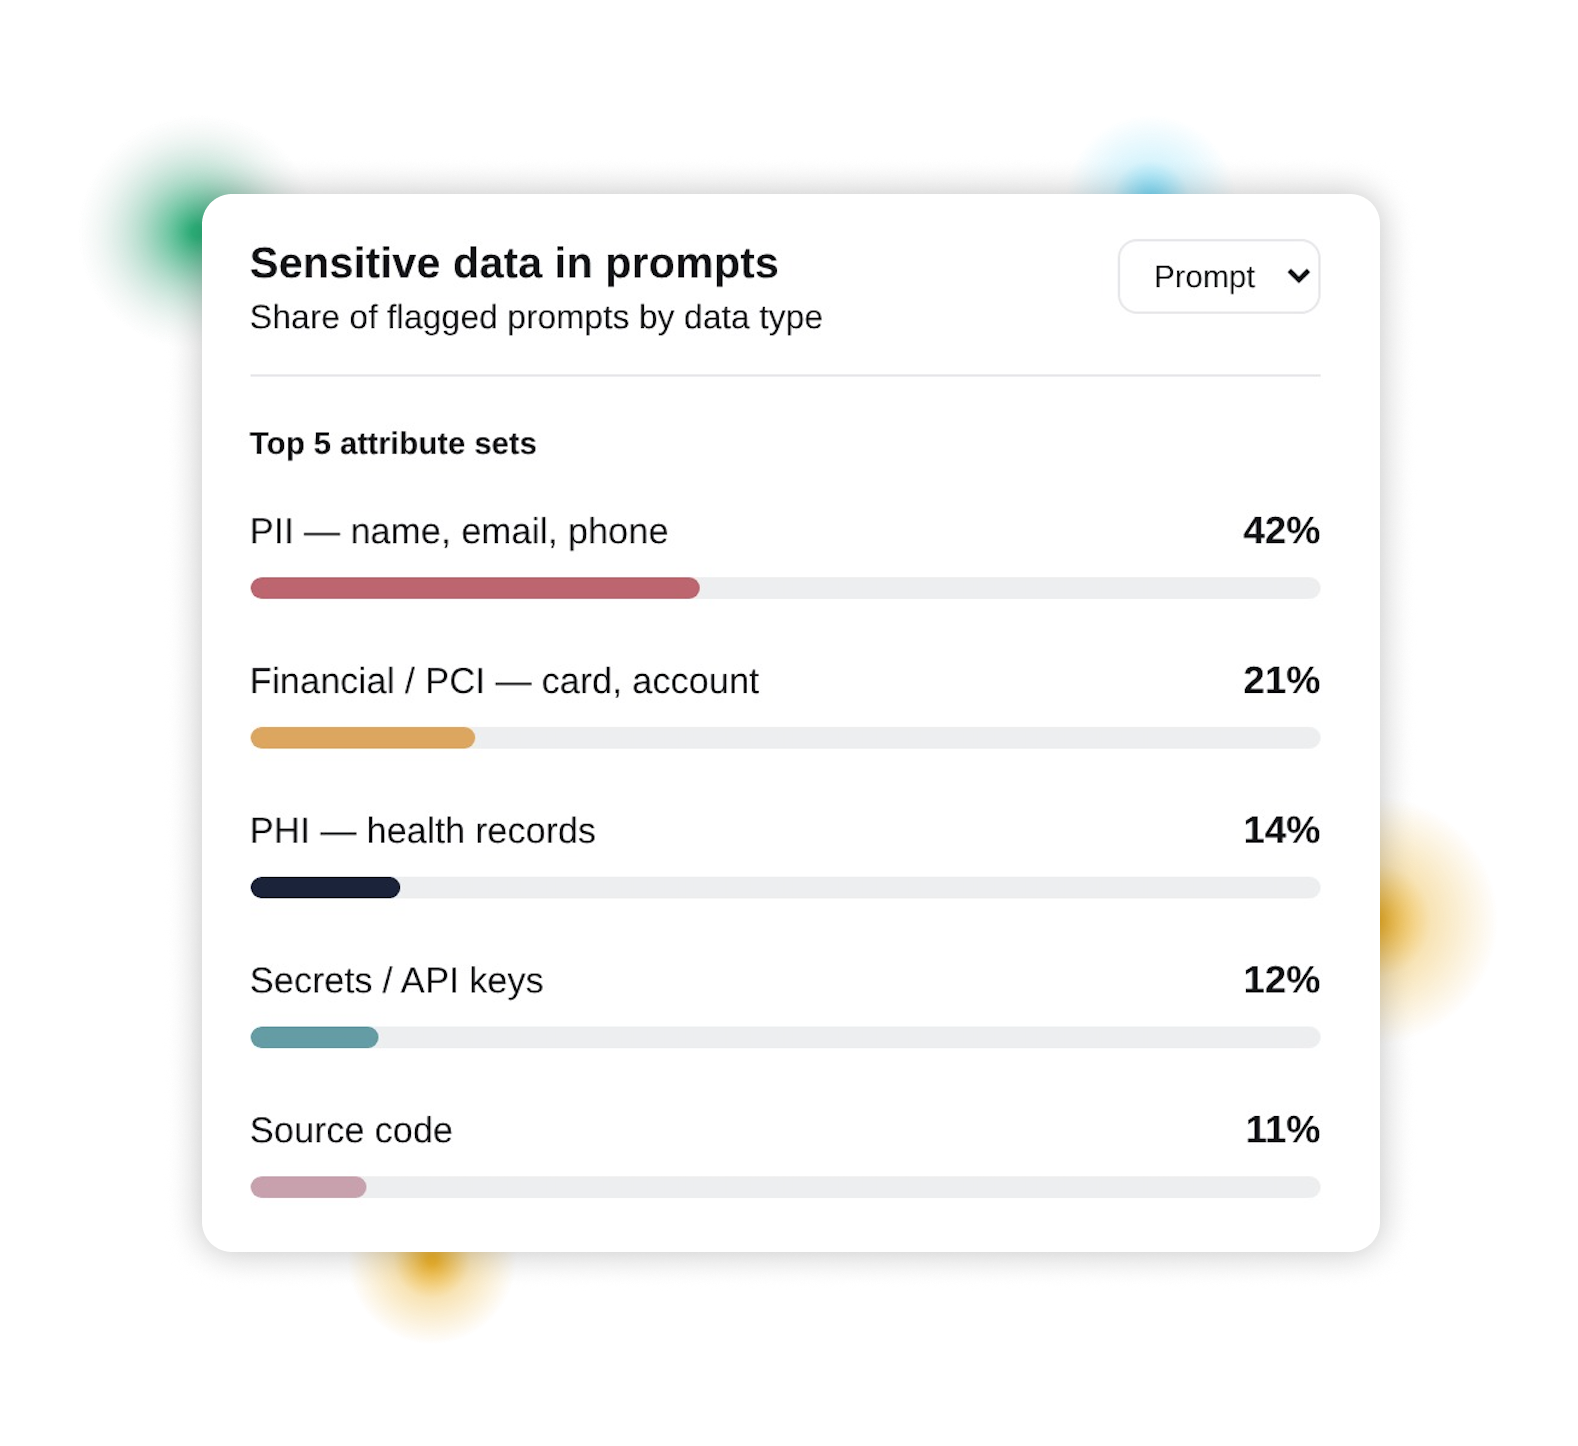
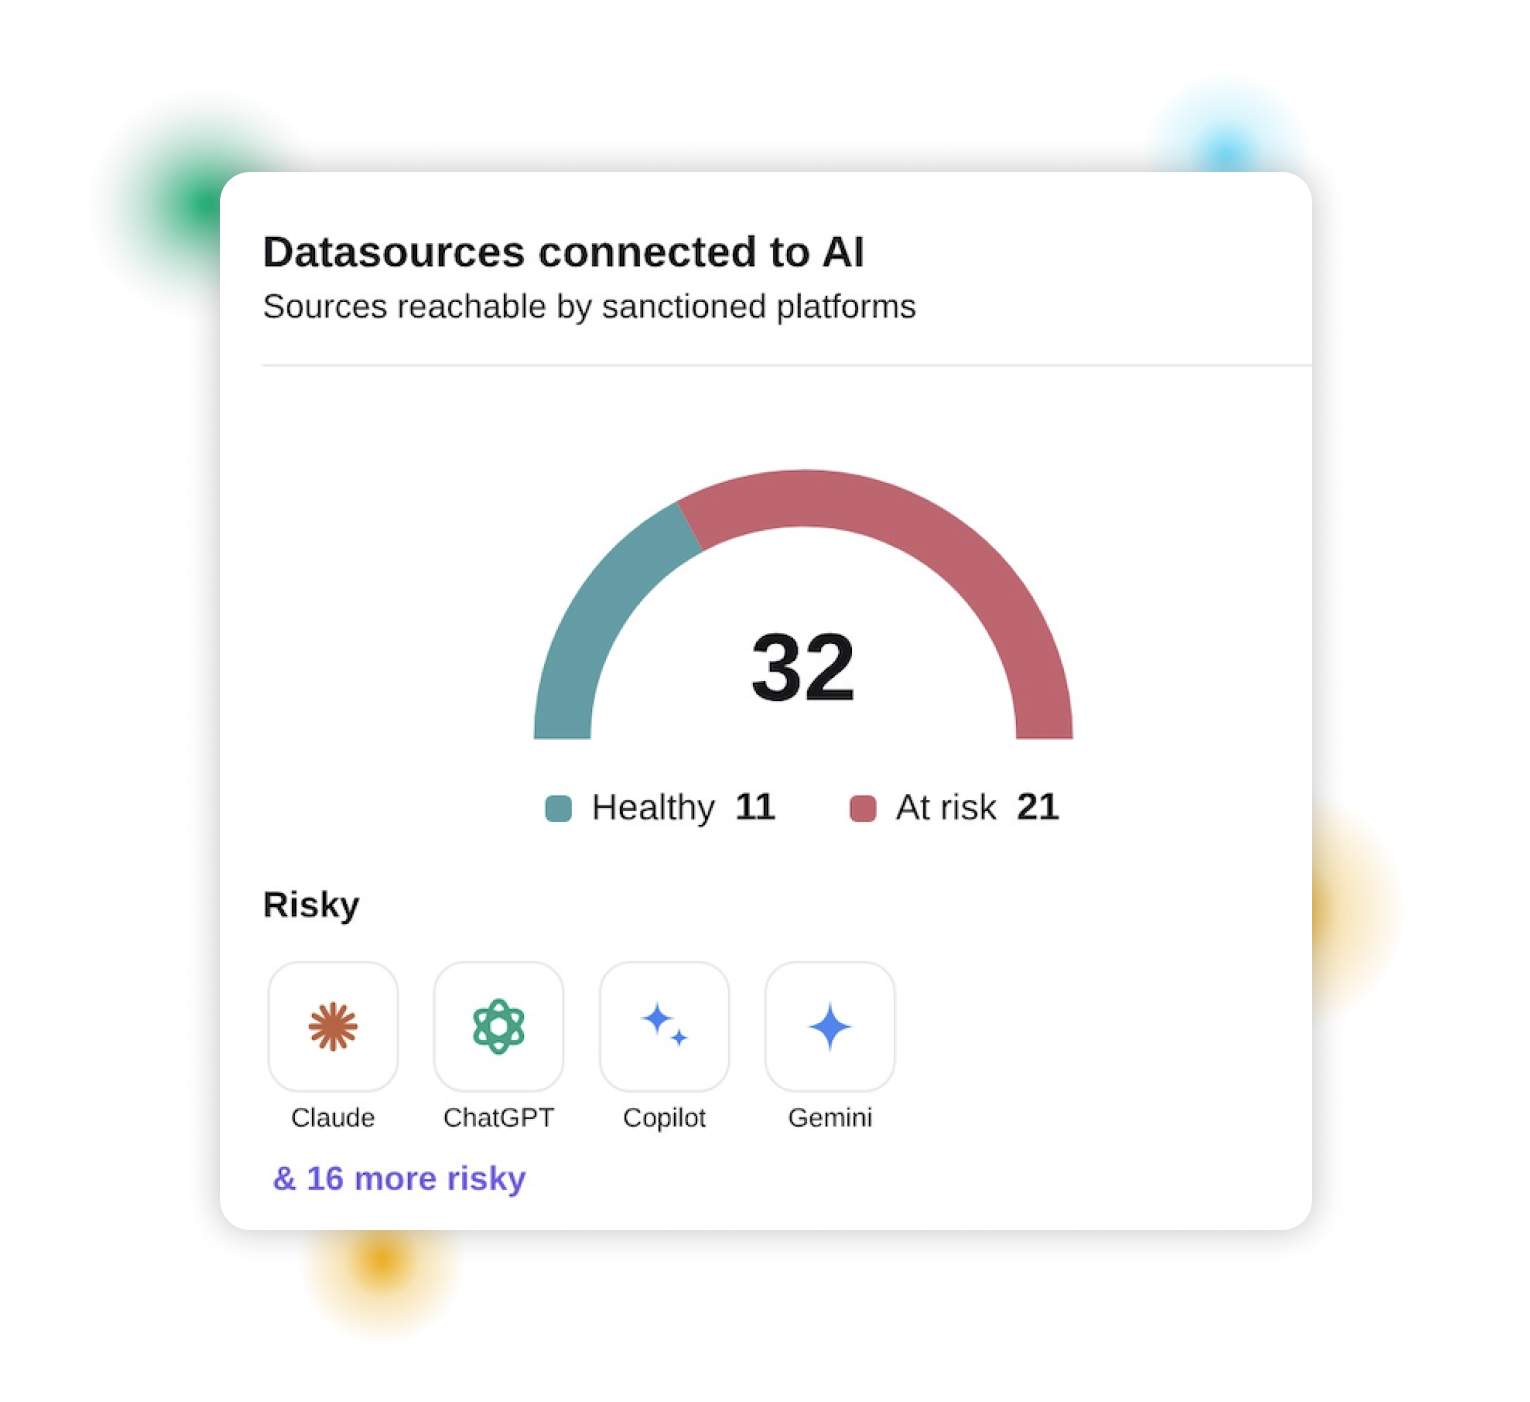
AI Governance With Data, Identity and Purpose Context
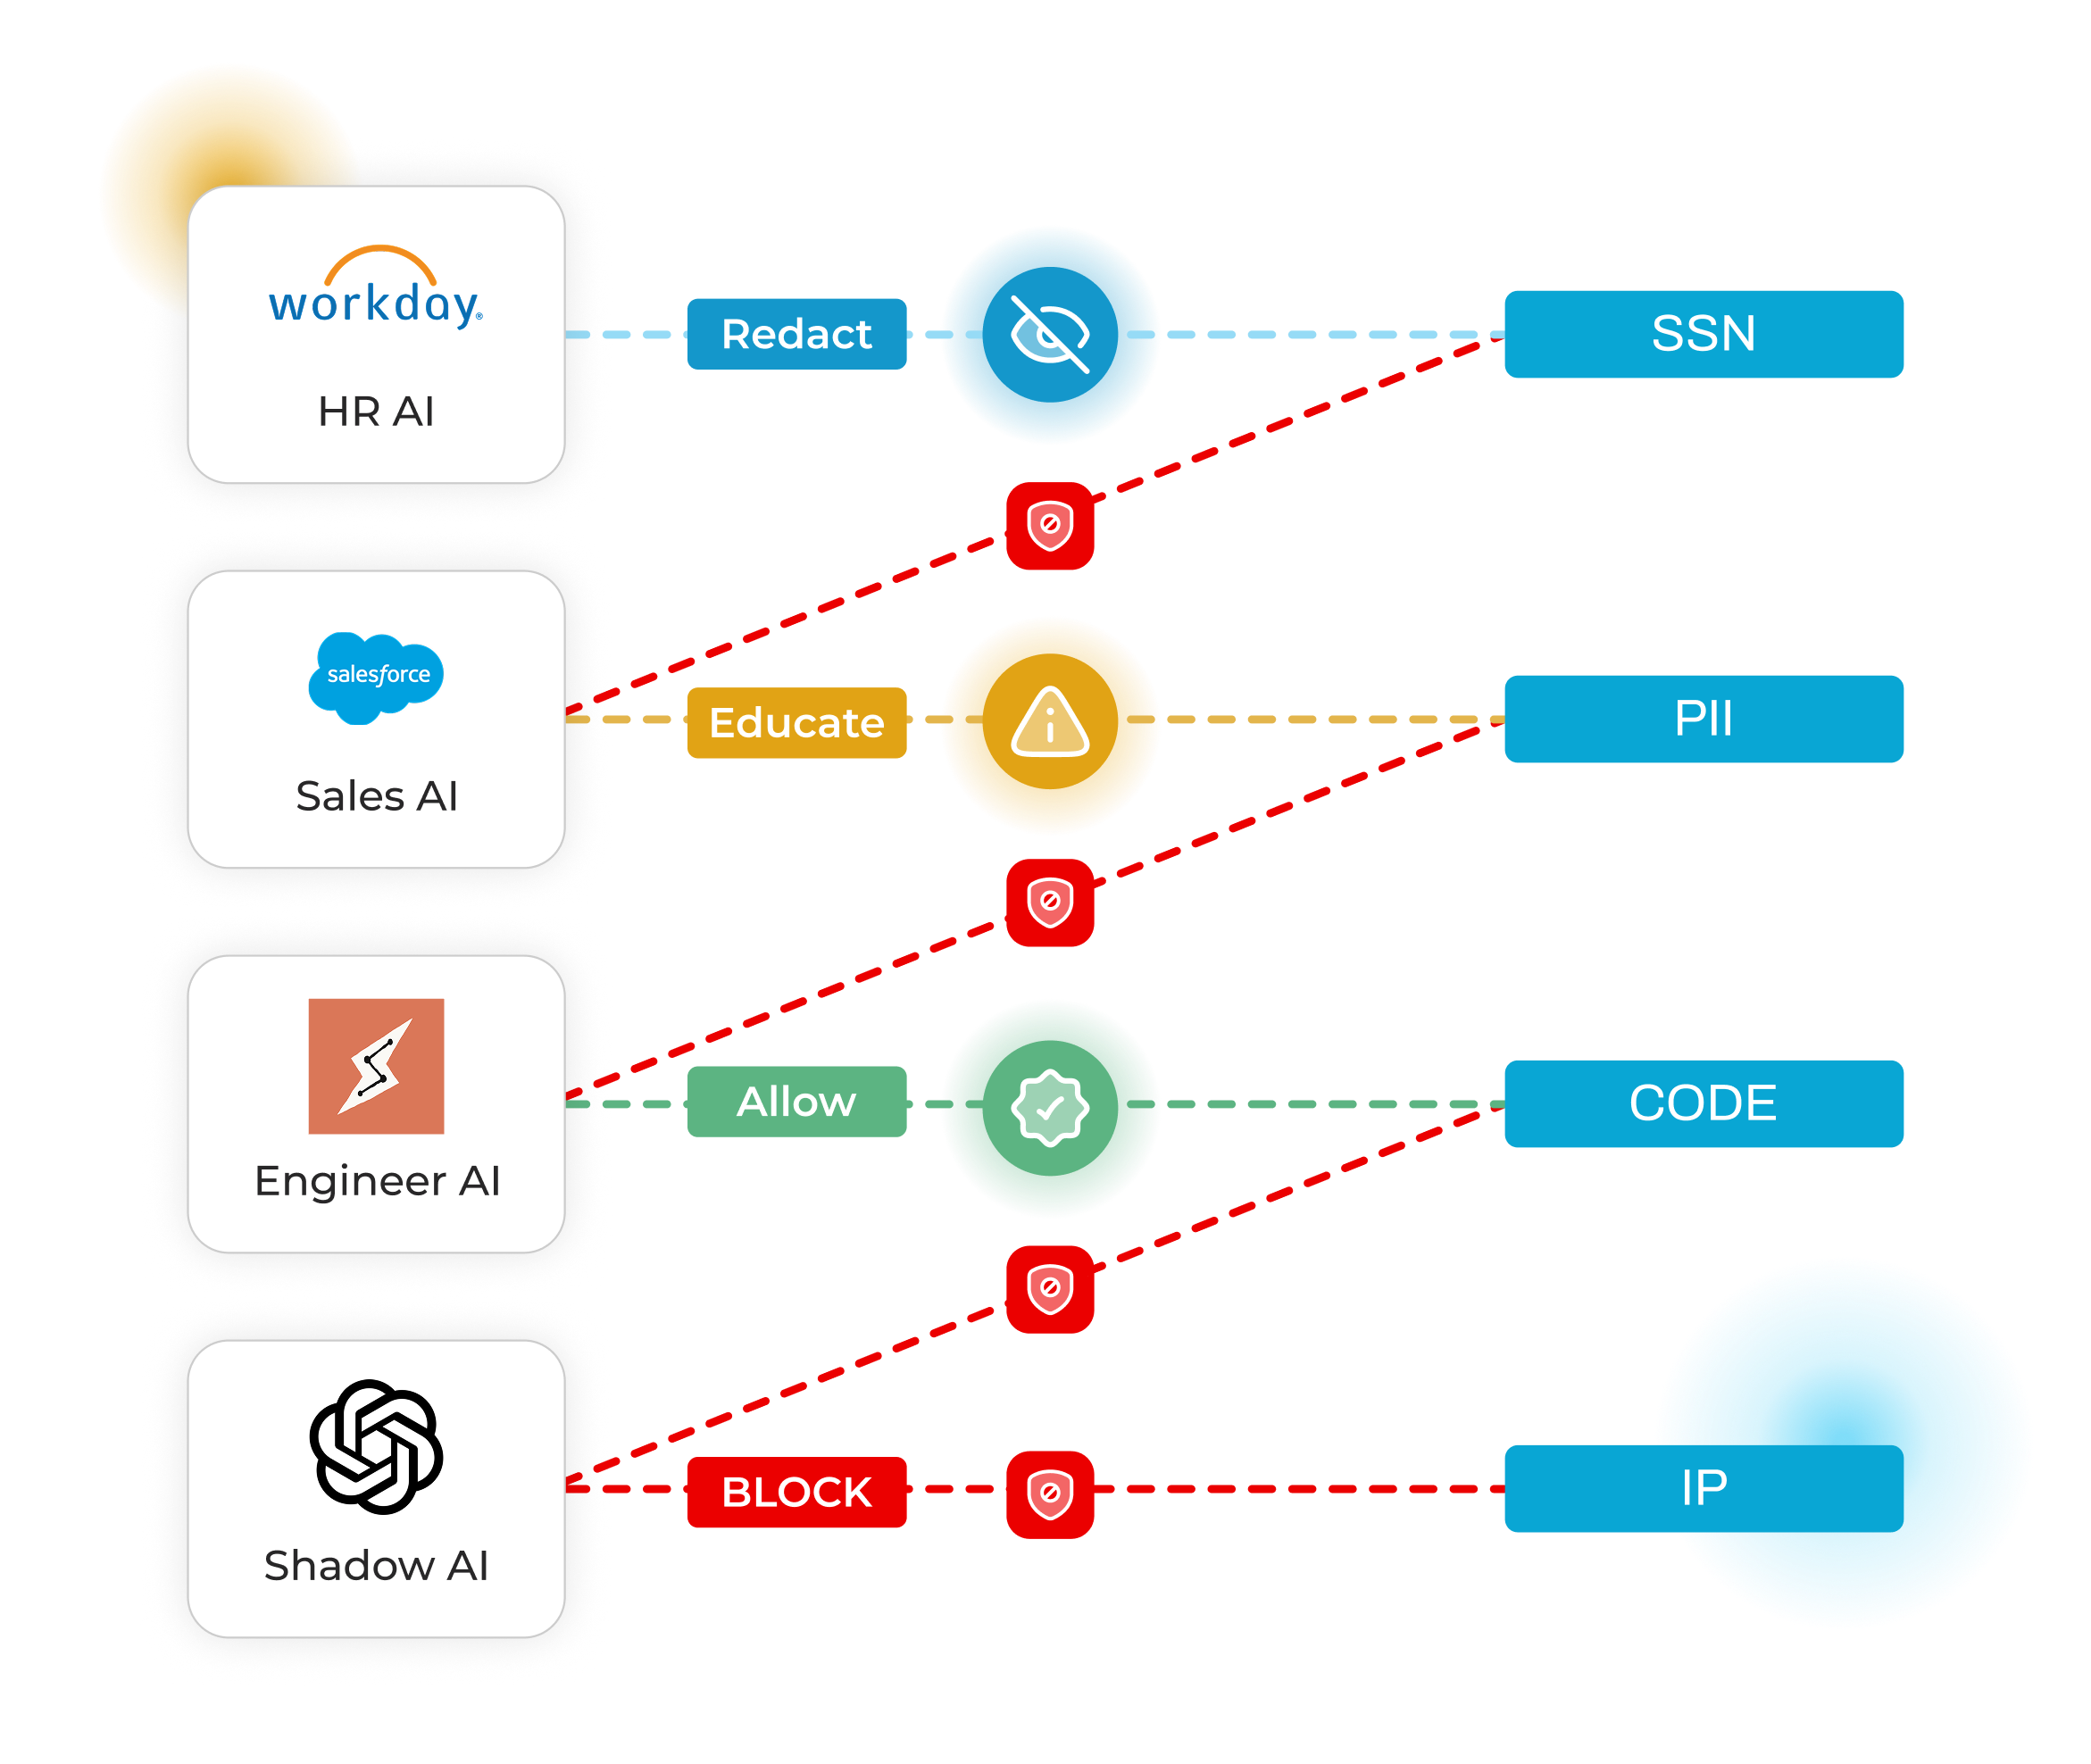
Lightbeam discovers sensitive data, maps it to human and nonhuman identities, evaluates access against intended purpose, and continuously remediates excessive access to enforce Least Agency.
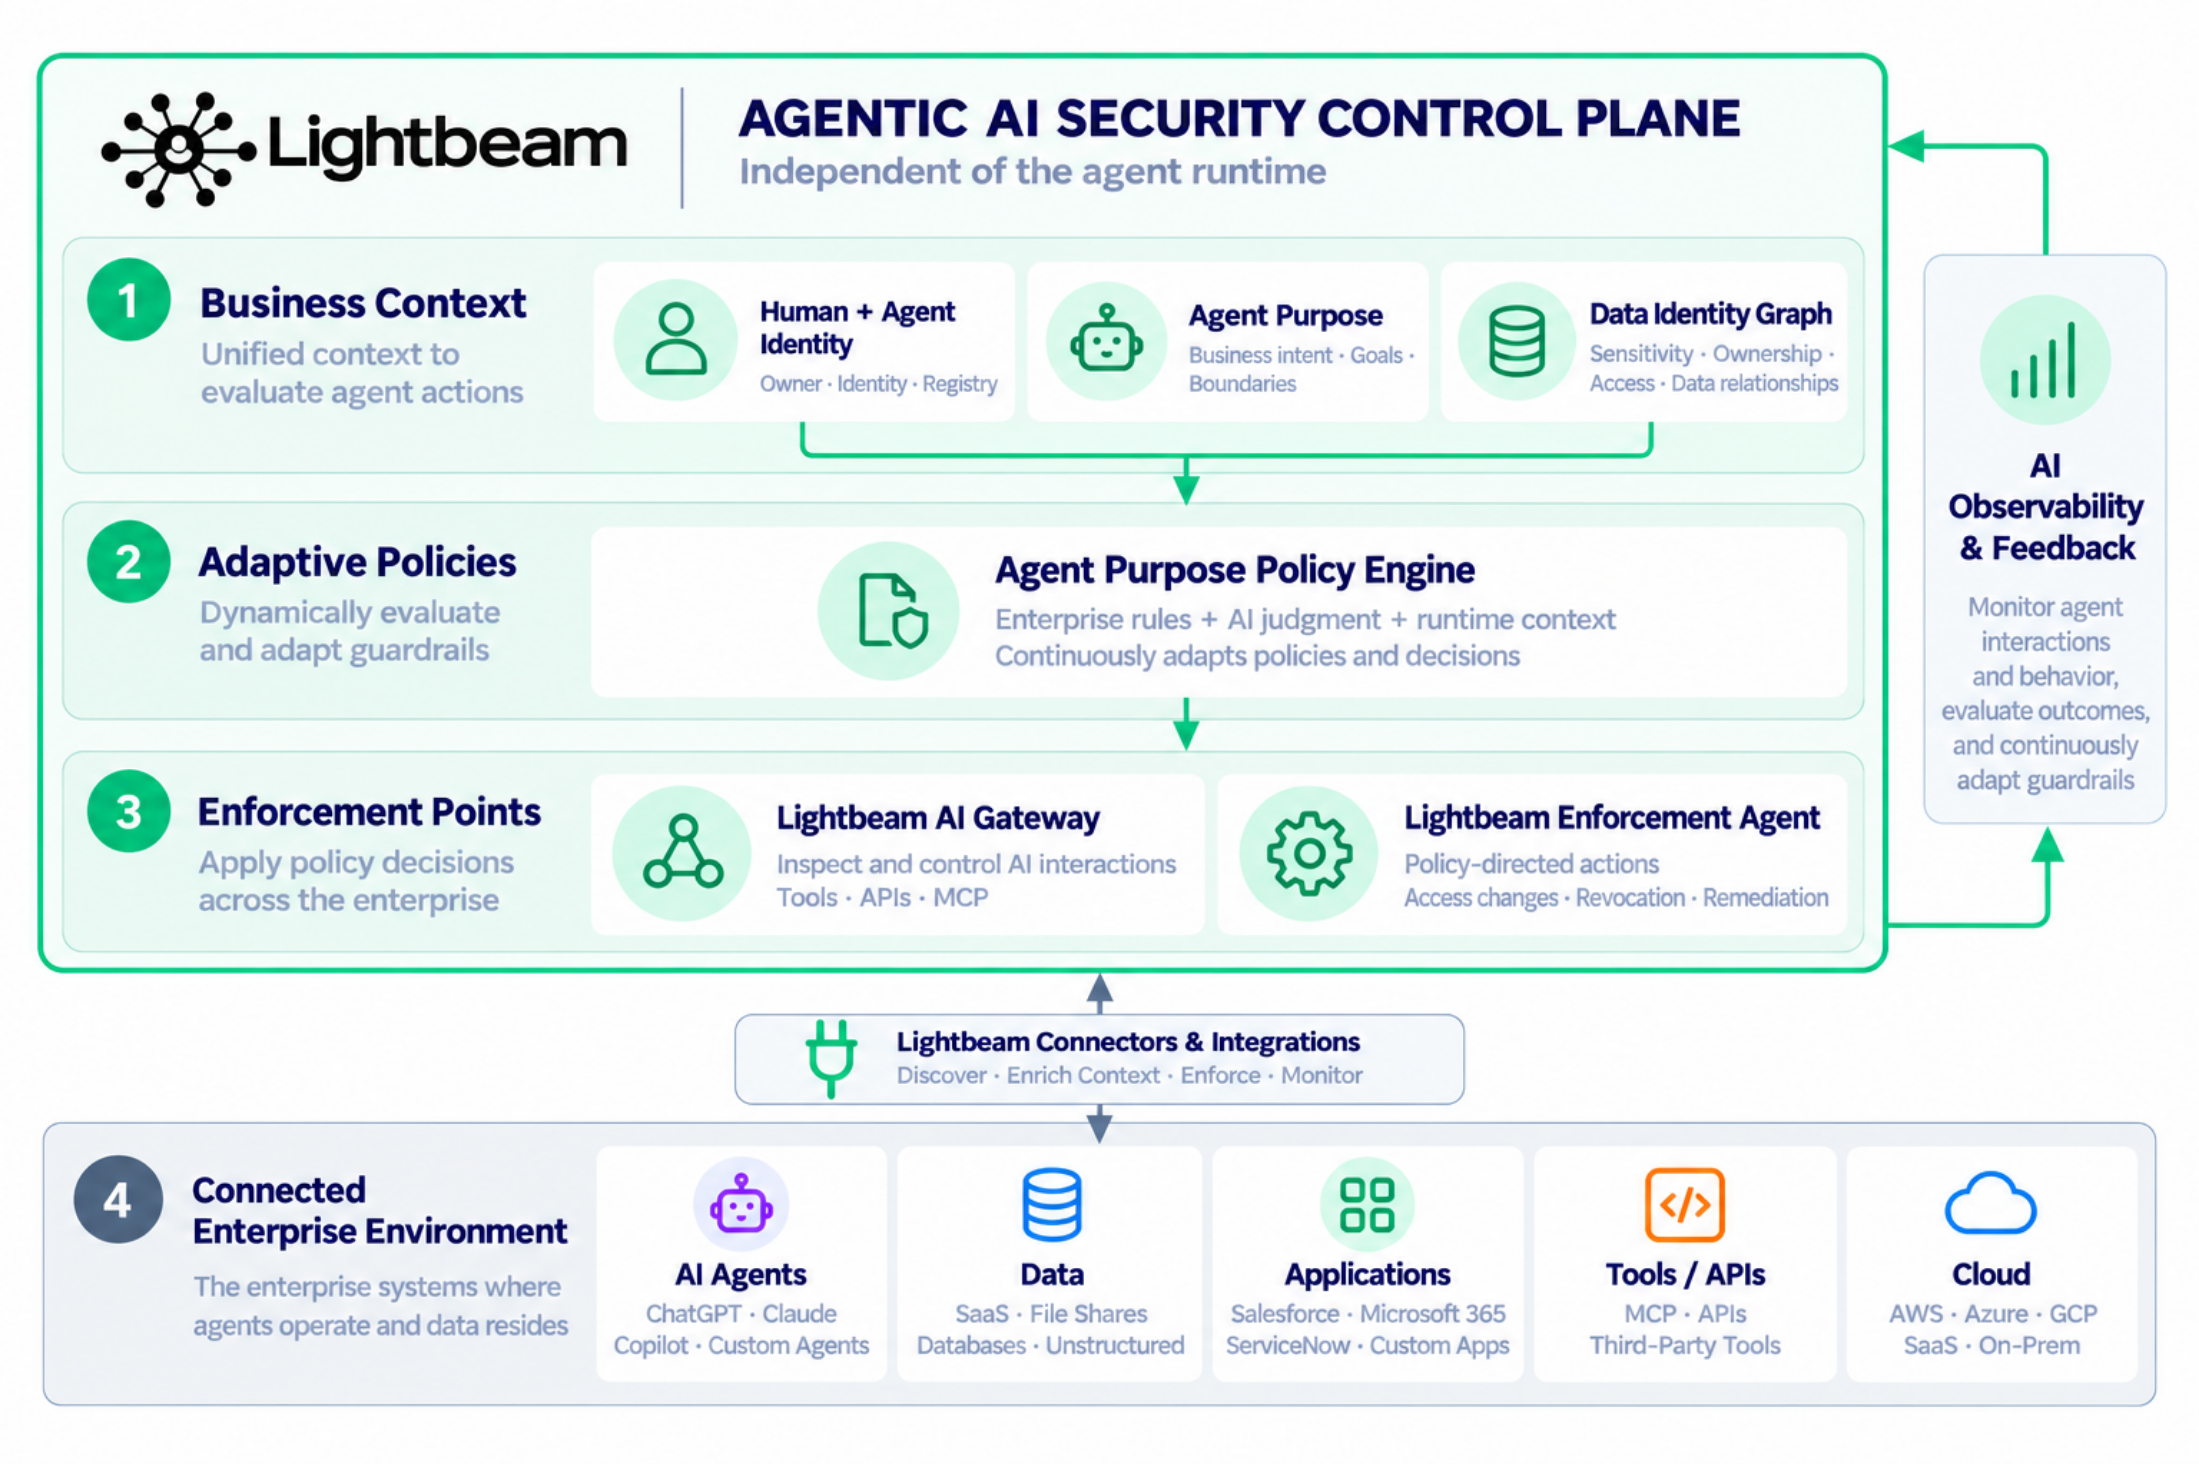
See what else the Lightbeam platform solves
AI Security
Enforce Agent Purpose across sensitive data, agent privileges and runtime actions, from employee AI tools to autonomous workflows.
Learn MoreData Classification
Discover and classify structured and unstructured data, surface risk and reduce exposure at scale.
Learn MoreUser and Entity Behavior Analysis
Lightbeam detects insider risk by baselining user behavior on sensitive data, then flags and remediates threats, showing who’s at risk, what moved, and why.
Learn MoreData Security Posture Management
Lightbeam discovers shadow data, maps risk, and automates remediation so security teams gain clear control and compliance.
Learn MoreCustomers who love their results
“What we want to make sure we’re able to do is protect data from AI use that could cause a security risk. If we want to restrict sensitive data, we need the ability to identify it and put policies in place that don’t allow that AI system to access it, while maybe allowing access to other information that can help automate tasks or analyze data.”

“Lightbeam gives us the ability to scan, classify, categorize, and label data so we can ensure that data does not go into areas it does not need to, including AI models.”
Quick Answers
Frequently Asked Questions
What is AI Governance, and how does Lightbeam help enterprises govern autonomous AI agents?
AI Governance establishes the policies, accountability, and oversight needed to safely deploy GenAI and autonomous agents. Lightbeam connects Agent Purpose with data, identity, and access context to govern what agents can use, reach, and do. Adaptive policies and AI Usage Control help enforce business boundaries and maintain accountability as AI adoption scales.
Explore AI SecurityHow does Lightbeam enforce least agency and purpose-based access control for AI agents?
Least agency extends traditional least privilege beyond data access to the tools, decisions, and actions an agent can perform. Lightbeam evaluates each agent's intended business purpose and continuously aligns access to the data, applications, APIs, and resources needed for its tasks. Excessive privileges can be restricted or revoked, with approvals required for higher-risk activities.
Explore the Lightbeam PlatformWhat is the difference between AI Governance and AI Usage Control?
AI Governance defines the business purpose, policies, responsibilities, and oversight for GenAI and autonomous agents. AI Usage Control puts those policies into action by monitoring AI interactions and agent behavior, restricting inappropriate data use, enforcing access boundaries, and blocking harmful actions. Together, they enable trusted autonomy while preserving enterprise security and accountability.
Explore AI Data SecurityBrowse Key Resources

Ready to reduce AI data risk?
See what sensitive data AI can reach, whose data is exposed, and which actions will reduce risk fastest.